CRA templates for manufacturers of industrial products
Don't build your CRA documentation from scratch.
Editable Word templates, Excel sheets, process descriptions, RACI matrices, mapping tables and checklists for manufacturers of machinery, production systems, embedded systems and industrial products.
For companies that already work on product security, IEC 62443, vulnerability management or technical documentation but have not yet turned that work into a CRA evidence structure that holds up.
Buy single modules or the full package. Indicative pricing within 24 hours.
Secuvise in numbers
350+ Compliant Products
Developed from audit, certification and implementation projects with industrial manufacturers.
40+ Manufacturers Supported
Experience from more than 40 manufacturers of products with digital elements.
Aligned with the standards
Built around IEC 62443-4-1, CRA evidence requirements and CE technical documentation.
What you get
Included in the package
- Approx. 120 pages of editable process documentation
- 15+ Word and Excel templates
- 8 mapping tables from CRA requirement to evidence
- RACI matrices for engineering, product security, QM and product management
- Checklists for implementation, review and evidence
- Optional: kick-off workshop or review of your adapted templates
What it changes for you
Your teams agree faster on which processes are missing, who owns them, which evidence you need and which documents belong in the technical documentation.
Pricing: Buy modules individually or get the full package with an optional kick-off workshop. You'll have indicative pricing within 24 hours.
A good fit if …
This sounds like you
- You manufacture products with digital elements
- You need to turn CRA requirements into processes and technical documentation
- You already run security activities but have no end-to-end evidence structure
- You want to connect IEC 62443-4-1, product security, QM and CE documentation
Who usually reaches out
- Product security managers
- Heads of engineering
- Product managers responsible for conformity
- QM and compliance teams working with engineering and CE
Not a fit if you are only looking for general CRA training or you have no obligations as a manufacturer.
CRA reporting obligations have applied since 11 Sep 2026, not 2027
Under Regulation (EU) 2024/2847, the full CRA requirements apply from 11 December 2027. But manufacturers already have obligations today: since 11 September 2026, they have had to report actively exploited vulnerabilities and severe incidents. Isolated security activities won't cover that. You need defined processes, roles, decision-making, escalation, documentation and evidence. The CRA template package is built for exactly that.
Since 11 Sep 2026: reporting obligations
You must be able to report actively exploited vulnerabilities and severe incidents. Without a working process today, you risk missed deadlines and the liability that comes with them. This also covers products you have already placed on the market.
11 Dec 2027: full CRA application
From this date, all core obligations of the Cyber Resilience Act apply, including evidence and conformity assessment.
The usual situation: security in place, evidence missing
Security with gaps in the lifecycle
Security activities are running, but not consistently across the entire product lifecycle.
Documentation not audit-ready
Documentation exists, but not in a form a conformity assessment body will accept.
Unclear ownership
People know who is responsible, but it is not clearly documented or agreed across departments.
What is usually missing is the link between requirements, processes, responsibilities and evidence. The template package provides that link.
Modular: start where it hurts most
Buy the full package or individual modules. Start where the pressure is highest and add the remaining modules later.
Governance & responsibilities
- Roles and responsibilities across the product lifecycle
- RACI matrices for engineering, product security, QM and product management
- Alignment between engineering, QM and management
Development process & SDLC
- Secure development process following IEC 62443-4-1
- Security requirements, secure design and implementation
- Verification, testing, risk assessment and threat modeling
PSIRT, vulnerabilities & reporting
- Vulnerability management and disclosure
- Incident response and escalation
- Reporting processes for the deadlines that have applied since 11 Sep 2026
Suppliers & third-party components
- Requirements for suppliers and supplied parts
- Handling third-party and open-source components
- Evidence along the supply chain
Infrastructure, DevOps & updates
- Update and patch management
- Development, build and production environments
- Support period, end of support and end of life
Included in every module
Every module includes templates for the technical documentation and the EU declaration of conformity, tables that map each CRA requirement to its evidence, and checklists for implementation, review and evidence.
Buy modules individually or get the full package with an optional kick-off workshop. Indicative pricing within 24 hours.
Get the overview and pricingExamples from the package
How the templates are built: schematic views of selected artifacts from the package.
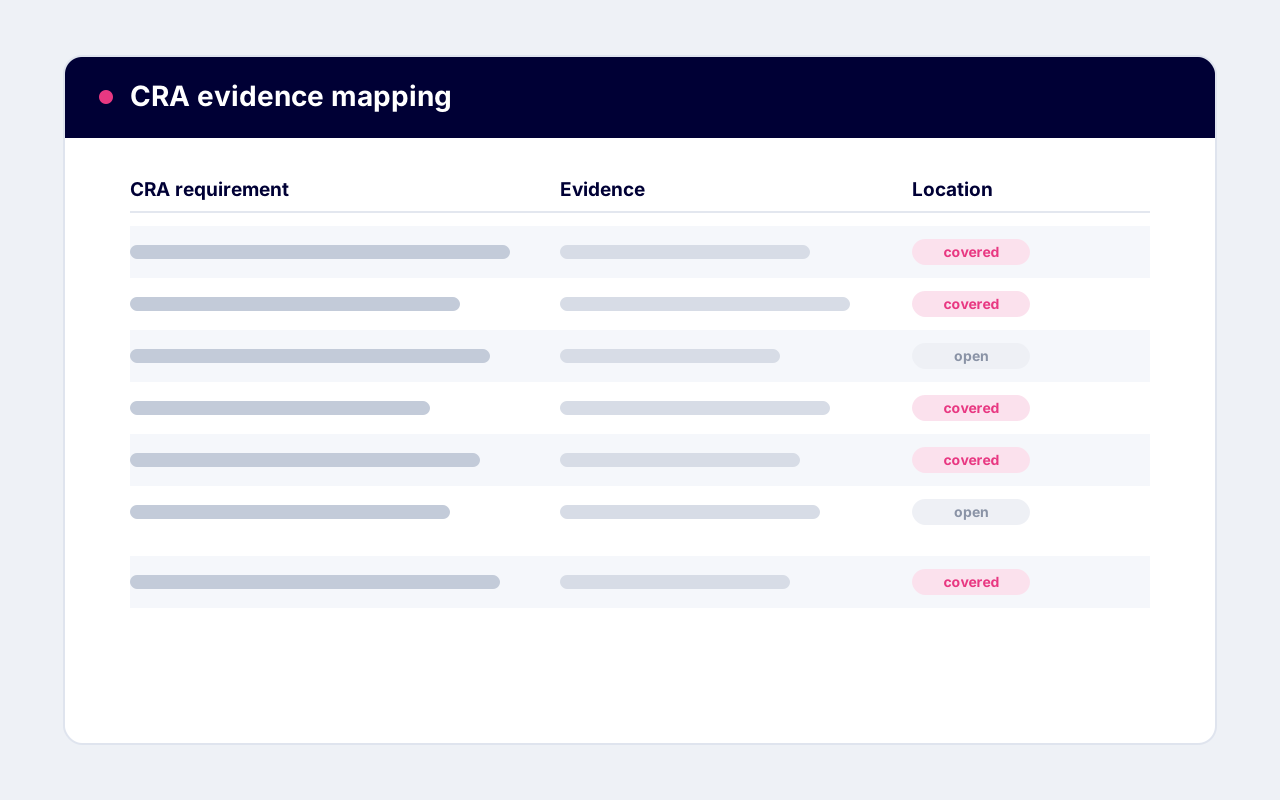
CRA evidence mapping
Maps each CRA requirement to a specific piece of evidence and where to find it.
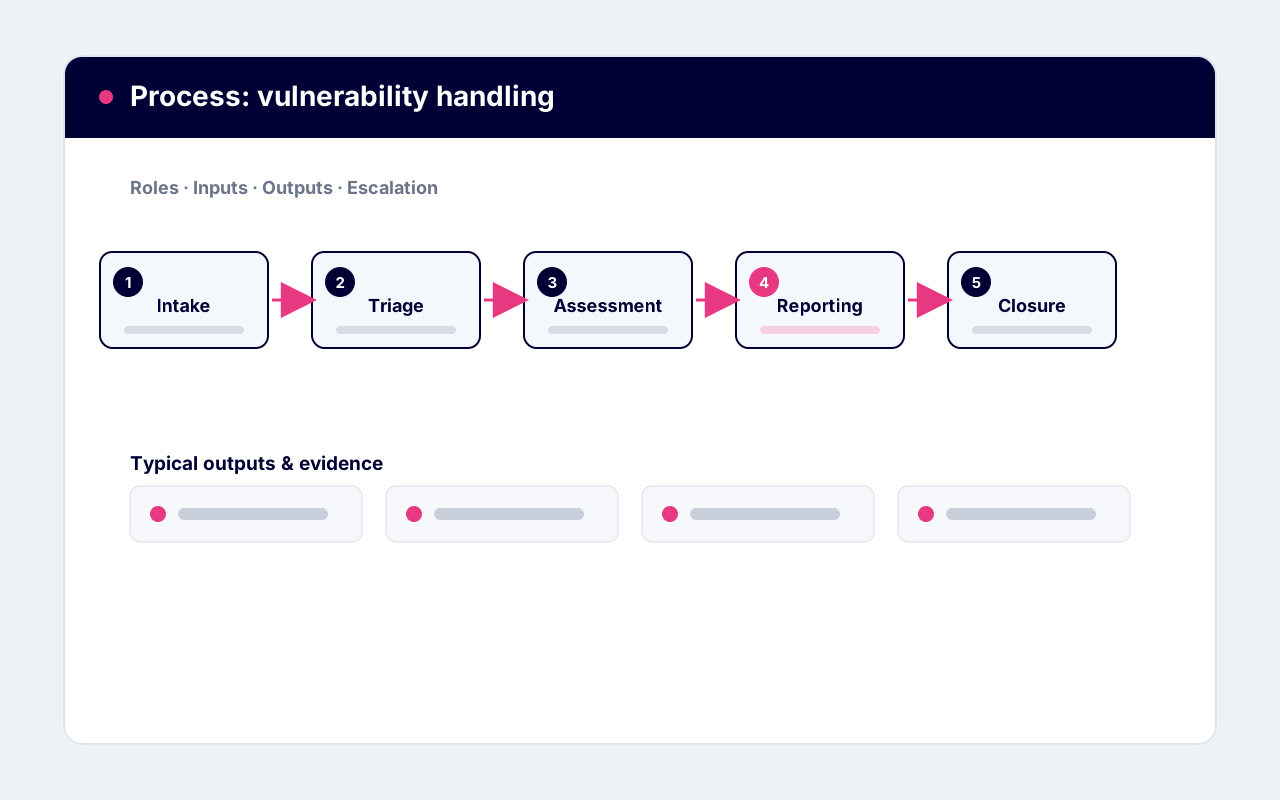
Process: vulnerability handling
Process description with roles, inputs, outputs and escalation.
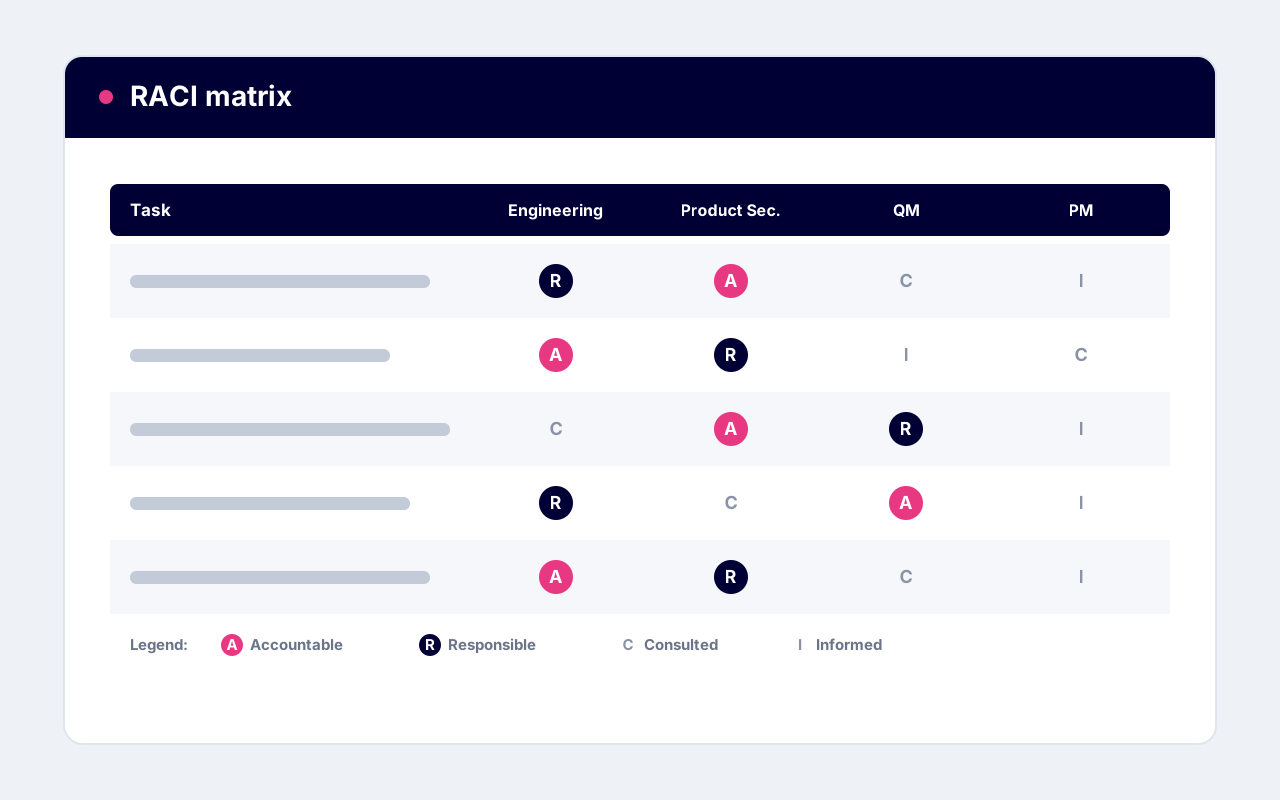
RACI matrix
Responsibilities across engineering, product security, QM and product management.
Checklist: technical documentation
A checklist of every document that belongs in the technical documentation.
Evidence review checklist
Sanity-checks your artifacts before a third party reviews them.
Request sample excerpts
We'll send sample excerpts along with the package overview.
How you can use the package
On your own
You adapt the editable templates to your processes yourself and use the mapping, RACI and checklists as your framework.
With a review
We review your adapted templates and evidence for gaps and inconsistencies before they go into conformity assessment.
With a workshop or ongoing support
A kick-off workshop, or implementation support across several project phases if you would rather not handle it alone.
Why these templates
Practical tools for engineering teams
Many CRA materials quote requirements or describe ideal processes that real engineering organizations rarely put into practice.
The aim is documentation that fits how your teams actually develop products and still covers what the CRA, IEC 62443-4-1 and conformity assessment require. Paper processes nobody follows are no use to you.
Proven in projects
Developed from audit, certification and implementation projects, built around processes and evidence that work in practice.
For machinery, plant engineering and industrial products
Designed for long product lifecycles, complex supply chains, embedded systems and CE-marked products. Not written for pure cloud SaaS.
Based on IEC 62443-4-1
An established process model for secure product development that makes your processes auditable and ready for certification, even if certification isn't your goal.
Adaptable, not generic
Editable and structured so you can fit them to your existing processes and get from requirement to solid documentation faster.
Frequently asked questions
Do the templates replace legal advice?
No. They structure processes, roles, artifacts and evidence. The legal assessment itself depends on your company and product.
Are the templates enough for CRA compliance?
Not on their own. They help you build evidence that can be audited. Actual compliance depends on the product, its implementation, the risk assessment and the processes you apply.
Do the templates work for IEC 62443-4-1?
They follow the process model of IEC 62443-4-1 and can serve as the bridge to CRA evidence.
Can we buy a single module, e.g. vulnerability management?
Yes. The package is modular. Start with the module you need most urgently, for example PSIRT and reporting, and add the others later.
Are the templates suitable for machinery and embedded systems?
Yes, that is what they were written for: manufacturers of industrial products with long lifecycles, rather than pure SaaS or consumer software vendors.
Can Secuvise review our adapted templates?
Yes. As an option, we review your adapted templates and evidence for gaps and inconsistencies. A kick-off workshop and implementation support are also available.
Prefer to talk?
Book a 30-minute call. We'll work out which modules fit your situation.
Book a 30-minute callRequest the package overview
Modules, formats and pricing at a glance
Request the package overview. We'll send you the module overview, formats, use cases and indicative pricing, usually within 24 hours. If it helps, we can take 30 minutes to work out which modules fit your situation.
Your details
We'll send you the module overview, formats and indicative pricing.